AI GOVERNANCE · GOVERN
FairPath
The AI governance workbench.
THE GOVERNANCE GAP
Sound familiar?
- Governance lives with legal and every answer is no — because blocking is easier than controlling.
- Nobody at leadership level can say, with confidence, which AI systems are running, what they decide, and who owns that risk.
- Fairness is asserted, not evidenced; documentation is scattered across drives; the auditor’s first question has no answer.
- The regulation moves and nobody notices until a deadline has passed.
WHAT YOU GET
Map it · Run it · Prove it
Audit-ready AI governance in one place: every classification, risk, control and incident documented with its rationale — and fairness evidence a third party can verify without trusting us. Three ways to run it — pick the depth your obligations require. Every tier includes the consulting to make it work.
FairPath Mini
Map it
- Maturity assessment
- AI system inventory
- Risk-tier classification
- Legal obligation checklist
FairPath Standard
Run it
- Everything in Mini
- Governance framework (RACI, cadence)
- Per-solution risk and impact assessment
FairPath Premium
Prove it
- Everything in Standard
- Full policy framework and principles
- Controls, audit, incident management
- Regulatory monitoring
- + ISO/IEC 42001 implementation, AI audit, Governance Lead and DPO — available as add-on services
FEATURES
- AI system inventory with organisation role (provider / deployer / both) driving obligations
- EU AI Act classifier — Art. 5 prohibited, Annex III / Annex I high-risk, Art. 6(3) exemptions, profiling, Art. 50 transparency; obligation lists sized by tier and role, reasoning shown
- Risk register — categories, impact × likelihood, inherent and residual scores, risk appetite, documented treatments, controls
- Fairness testing and evidence — proxy detection, adverse impact (four-fifths rule), full-label fairness metrics, significance tests, intersectional analysis; a signed evidence bundle (SHA-256) a third party can verify without FairPath
- ISO/IEC 42001 controls — 38 controls in 9 groups, effectiveness, test methods, evidence, corrective actions; crosswalk AI Act obligations ↔ ISO controls
- Governance — charter with RACI, 6 policy templates with lifecycle and Word export, 12 ethics principles, documentation register, QMS manual · maturity assessment — 100 questions, 10 domains · DPIA / FRIA with gating and pre-fill
- Incident management with AI Act serious-incident deadlines (15 / 10 / 2 days) and notification letters · regulatory monitor querying the EU Publications Office at source — “unknown is not no change”
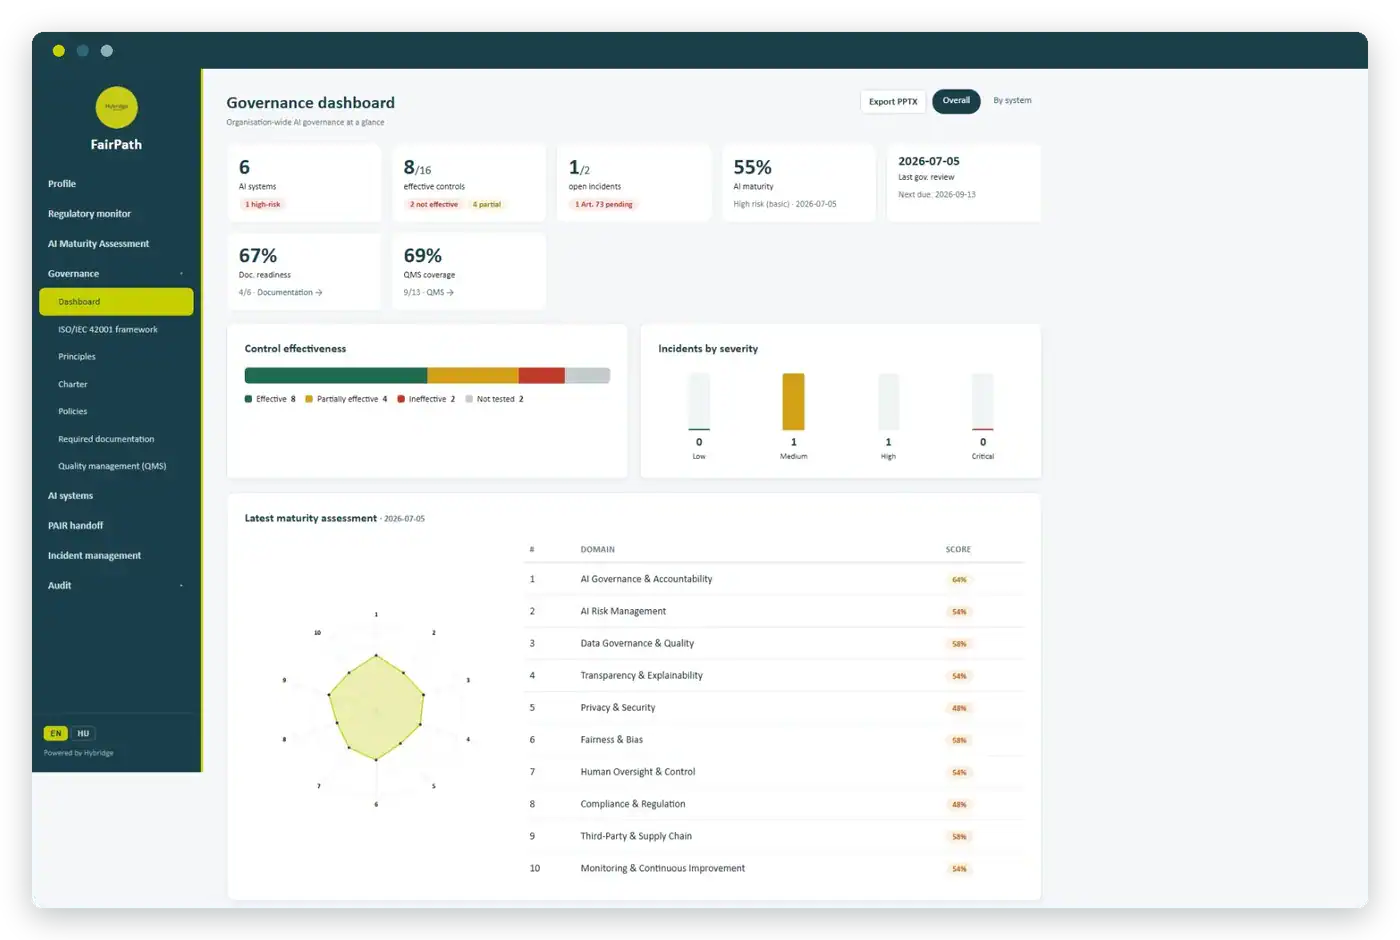
- Governance dashboard with PowerPoint export · audit reviews with findings and history · pAIr handoff · an AI assistant that only suggests — never calculates, never decides · English and Hungarian interface and documents
WHERE IT SITS
Between pAIr (decide) and gAIn (plan): FairPath governs what gets approved, evidences what gets deployed, and monitors what the regulator changes.
SEE IT IN ACTION
HOW TO START
Start small. See it working before you commit.
AI Governance Quick Scan
A personalised readiness result — the baseline your roadmap builds on. Three minutes.
FairPath Mini
Map it: maturity assessment, AI system inventory, risk-tier classification and the legal obligation checklist — a fixed package plus an annual fee.
Say yes safely.
Consulting included. Seniors only. Documented, auditable methodology.